How to integrate email verification into a SaaS signup flow without blocking legitimate users
By SendBridge Team · Published Nov 17, 2026 · 7 min read · Email Deliverability
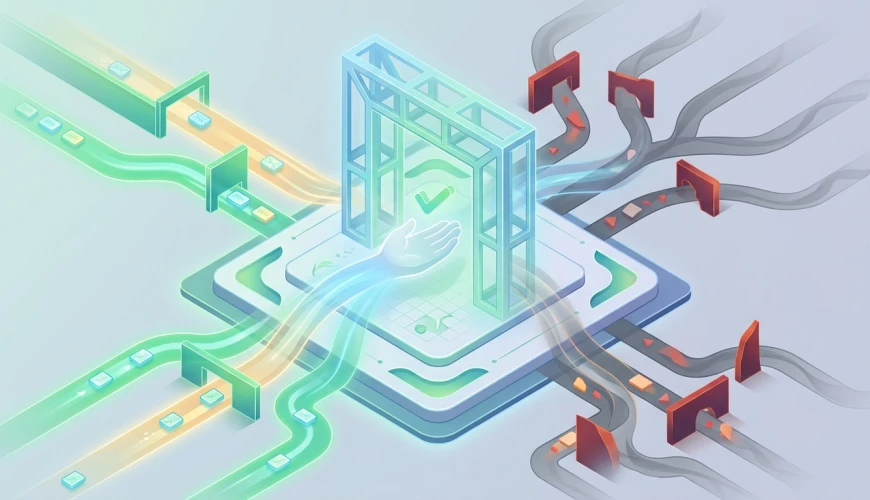
Email verification in a SaaS signup flow should behave like a bouncer who recognizes regulars – it stops typos and throwaway addresses, but waves real customers through without a second glance. The way to get there is combining a lightweight real-time check at the input level, a stricter server-side validation before account creation, and clear fallbacks for when your verification provider has a bad day. This article walks through the integration patterns that keep signups fast and your deliverability healthy, without turning a forgotten dot into a lost customer.
Why email verification API integration matters for SaaS signup flows
Every email address you let into your system has a cost. Invalid addresses trigger bounces that hurt your sender reputation, derail your onboarding emails, and quietly inflate your churn metrics. A well-designed email verification API integration catches those problems before they reach your database.
Teams working with an offshore software development company USA often share responsibility for signup and authentication flows – Digis provides custom software development, API integration, and staff augmentation services. When your frontend engineers and your API team sit in different time zones, having one documented verification pattern becomes essential, because a mismatch between the browser and the server can block real users in ways nobody notices for weeks.
It is also worth being precise about what verification actually proves. An email verification API assesses address quality and deliverability signals. A confirmation link establishes whether the user can access the mailbox. Neither replaces the other. Good SaaS signup email validation combines both: checks that run before account creation to filter obvious garbage, and a confirmation step that proves the mailbox is reachable by the person who signed up.
Common patterns that block legitimate users during signup
Over-aggressive validation is a frequent reason real users abandon a signup form. A few patterns show up again and again:
- Rejecting plus-addressing (user+tag@gmail.com) because a regex was written in 2011.
- Treating any new TLD (.dev, .io, .health) as suspicious.
- Blocking every address on a domain with no MX record, including freshly registered company domains.
- Using a single third-party blocklist as the source of truth with no manual override.
- Returning a generic "invalid email" message that leaves users guessing what went wrong.
Each of these feels safe until you open your signup analytics and notice a quiet drop at the email field. The goal is to warn, not to lock out. A yellow "did you mean user@gmail.com?" nudge is usually more effective than a red "invalid email" wall.
Combining instant feedback with server-side email validation
Instant feedback and server-side email validation are not alternatives – they are layers of the same flow. The browser handles basic syntax and formatting checks so users see errors as they type. Calls to a third-party verification API, however, go through your server, because the API key must never ship in client-side code. Real-time email verification can absolutely happen while the user is on the page; the call simply originates from your backend rather than the browser, usually proxied through your own endpoint that returns a sanitized result.
| Check type | Runs in | Best for | Avoid using it for |
|---|---|---|---|
| Regex syntax | Browser (JavaScript) | Catching obvious typos | Final verdict on validity |
| Domain MX lookup | Server (API call) | Confirming the domain has configured mail servers | Treating absence of MX as proof of undeliverability – SMTP defines an implicit MX fallback |
| Disposable address list | Either | Reducing throwaway signups | Blocking privacy-conscious users |
| Role address flag (info@, admin@) | Server | Flagging for manual review | Automatic rejection |
An MX record tells you the domain has mail servers configured, but it does not prove that a specific mailbox exists on that domain. Set timeouts using measured provider latency and your signup response-time target. Define how pending checks, retries, and prolonged outages are handled before launch, rather than guessing numbers that read well in a design doc but break under real traffic.
Handling email verification service downtime without breaking signup
Every email verification service has downtime. If your signup flow goes down with it, you are giving your provider a veto over your business. The fix is a tiered response plan that treats failure as a normal operating condition.
A numbered sequence for handling email verification service downtime well:
- Measure provider latency in production and set per-call timeouts that fit your signup response-time target, not arbitrary figures.
- On timeout or 5xx response, log the failure and let the user proceed into a pending account state with defined restrictions – read-only access, limited feature scope, or trial-only data.
- Queue the verification for a background retry with exponential backoff.
- Before launch, document how prolonged outages are handled: a switch to a secondary provider, a fall back to a confirmation email link, or an admin-visible queue for manual review.
- Alert your on-call engineer based on sustained failure patterns rather than isolated timeouts.
This pattern keeps your signup flow working during an outage, at the cost of a few unverified accounts you can clean up later. The important detail is that a pending account must not automatically receive full product access – that is exactly how abuse rings exploit downtime windows.
Testing your email verification flow before and after launch
Signup verification testing is where many teams underinvest. You cannot wait for real users to find the edge cases, because by then your conversion is already damaged. Build a test matrix that covers valid addresses on major providers (Gmail, Outlook, Yahoo, iCloud), plus-addressed and dot-variant Gmail addresses, freshly registered custom domains with and without MX records, and known disposable domains for the negative case. Treat internationalized domain names (IDN, Punycode-encoded domains after the @) and non-ASCII characters in the local part before the @ as two separate support scenarios, because providers handle them differently and the failure modes are not interchangeable. Simulate rate-limit responses in automated tests, and use provider-approved test environments for live integration checks.
Automate these in your QA pipeline. If your stack is a React or Vue frontend, a Node.js or C# backend, and mobile clients on iOS and Android, your test harness can hit the verification API with the same payloads your real signup sends, then assert on both the response body and the time taken. Latency regressions are easier to catch in CI than in production, and a slow verification call often looks identical to a broken one from the user's side.
Pay attention to email verification error handling too. Every third-party API returns errors in its own format, and if your signup form surfaces the raw message, users see things like "SMTP greeting timeout" instead of a friendly nudge. Map every provider error to a short user-facing message, and log the original error for your own debugging. Users do not need to read your stack traces to finish signing up.
What to verify before launching the signup flow
Before you flip the switch on a new email verification integration, walk through a concrete pre-launch checklist tied to this topic rather than generic launch advice. Confirm that your API key lives only on the server and is rotated on a documented schedule. Confirm that the browser-side regex rejects clearly malformed input (missing @ or multiple @ characters, after trimming surrounding whitespace) but does not touch TLD lists or domain reputation. Confirm that the server-side verification call has a timeout grounded in the provider's measured p95 latency, not a round number pulled from a tutorial. Confirm that a timeout or 5xx response from the provider pushes the account into a pending state with limited scope, rather than either blocking signup outright or granting full access.
On the data side, confirm that logs record verification outcomes, error categories, and latency without exposing API credentials or unnecessary personal data. Confirm that confirmation emails use an authenticated sending setup, with delivery failures monitored and resend requests rate-limited. Finally, confirm that your manual-override path – the one that lets support unblock a real customer whose address was wrongly rejected – is actually reachable from the admin console and documented in your runbooks. Keep the flow open, keep the checks fast, and let your onboarding emails do the final confirmation work.